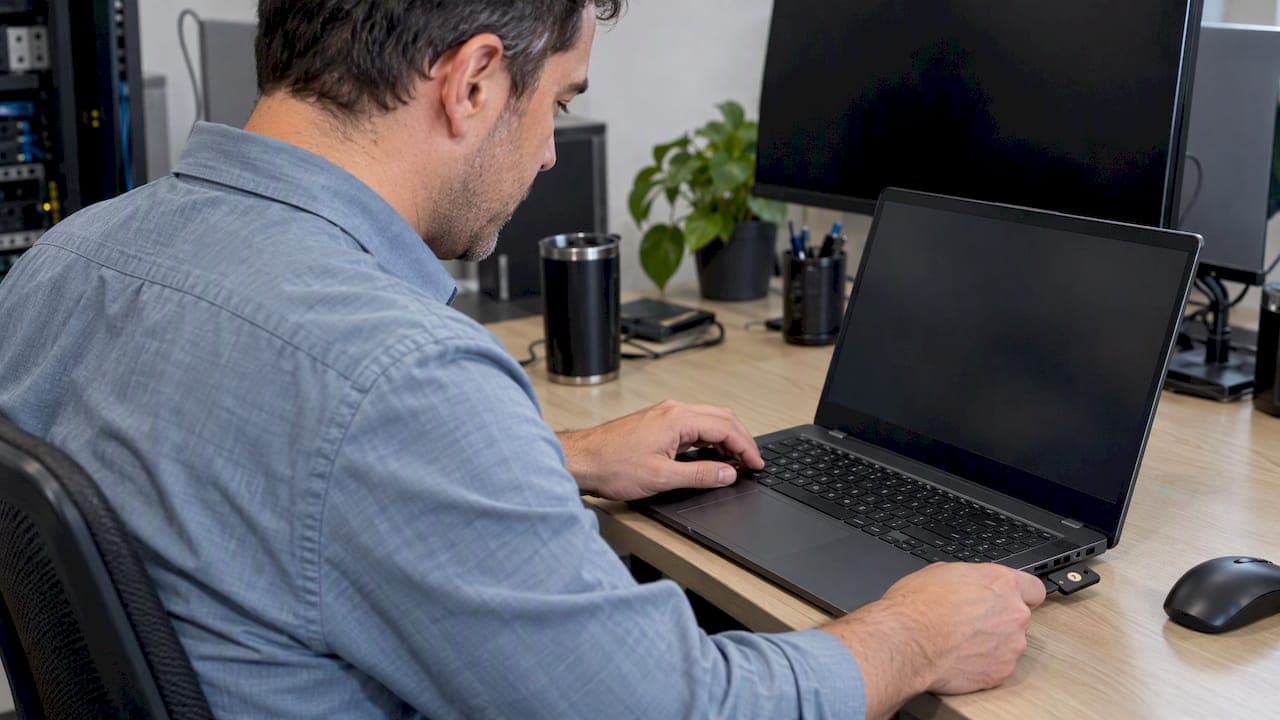
Three actions cut email risk faster than anything else: enable phishing-resistant multi-factor authentication for privileged accounts first, move your DMARC policy through monitoring to enforcement, and make phishing reporting a one-click habit backed by automated remediation. Everything else in a mature email security programme builds on these three controls.
TL;DR:
- Start with finance and executive accounts; enable FIDO2 keys or passkeys within 30 days, then extend phishing resistant MFA to all staff within 60–90 days.
- Keep DMARC at p=none for 30–60 days, check reports for clean alignment, and verify forwarding services and third party senders before enforcement.
- Run varied phishing simulations monthly, route one click reports directly to remediation, and track click rates, reporting time, and repeat offenders.
- Prepare a response playbook that revokes sessions, resets passwords, and purges malicious messages across mailboxes immediately; preserve evidence before logs disappear.
Table of Contents
- Quick actionable checklist: best practices at a glance
- Authentication and access controls
- Email authentication protocols: SPF, DKIM and DMARC
- User training and phishing simulations
- Detection and post-delivery remediation
- Incident response for email incidents
- Encryption and transport protection
- Policy, DLP and mailbox hygiene
- Nexus playbooks and how we help operationalize these controls
- A senior executive's take on sustaining email security
- Get help putting this plan into action
- FAQ
- Sources
Quick actionable checklist: best practices at a glance
Treat this as a working document. Assign an owner, a first step, and a timeline to each item, then revisit it monthly.
- IT security - enable FIDO2 or passkey MFA for admin and finance accounts; 30 days; impact: high.
- IT security - extend phishing-resistant MFA to all staff; 60 to 90 days; impact: high.
- IT admin - enforce SSO across email and connected apps; 30 days; impact: high.
- IT admin - disable legacy POP/IMAP/SMTP auth where business use allows; 45 days; impact: high.
- IT security - publish SPF and DKIM records for all sending domains; 14 days; impact: high.
- IT security - set DMARC to p=none and start collecting reports; 14 days; impact: medium.
- IT security - move DMARC to p=quarantine, then p=reject; 60 to 90 days; impact: high.
- HR/People - roll out role-based phishing training; 30 days; impact: medium.
- IT security - launch monthly phishing simulations with one-click reporting; 30 days; impact: medium.
- IT admin - enable breached-password screening; 30 days; impact: medium.
- IT admin - turn on external sender banners; 14 days; impact: low.
- IT admin - block auto-forwarding to external addresses; 14 days; impact: medium.
- IT security - deploy attachment sandboxing and URL rechecking; 60 days; impact: high.
- Leadership - approve an incident response playbook and a named response team; 30 days; impact: high.
Authentication and access controls
Credential theft remains the fastest path into a mailbox, and the fix starts with how people log in, not from another awareness poster.
Why phishing-resistant MFA matters. Traditional MFA (SMS codes, push approvals) still beats no MFA, but it is vulnerable to SIM swapping and push-bombing. CISA recommends phishing-resistant MFA built on FIDO or PKI standards, prioritized for administrators first, then expanded to other high-risk roles and finally the broader user base. Where a phishing-resistant method is not yet feasible, number matching on push notifications is a reasonable interim step.
Practical rollout steps:
- Inventory every account with mailbox or admin access, including service accounts.
- Enforce single sign-on so one hardened login gates access to email and connected apps.
- Disable legacy protocols such as POP, IMAP and basic SMTP authentication, which bypass modern MFA entirely.
- Screen new passwords against known breach lists and follow NIST's current guidance favouring length over forced complexity and frequent resets.
- Configure alerts on repeated denied MFA attempts, a common sign of push-bombing or credential stuffing.
Pro Tip: Start phishing-resistant MFA with your finance and executive accounts. They're the ones attackers target first for wire fraud.
SMS and app-based push MFA are better than nothing, but hardware keys and device-bound passkeys close the gap that SIM-swap and SS7 attacks exploit, and they align with what CISA's fact sheet on phishing-resistant MFA treats as the gold standard for privileged users.

Email authentication protocols: SPF, DKIM and DMARC
Spoofing a trusted domain is still one of the cheapest ways to run a phishing campaign, which is why SPF, DKIM and DMARC exist as a layered defence. NIST's technical note on email authentication describes SPF as authorizing which servers may send on your behalf, DKIM as a cryptographic signature proving message integrity, and DMARC as the policy layer that tells receiving servers what to do when either check fails.
Recommended sequence:
- Publish SPF records covering every legitimate sending source, including marketing and support tools.
- Add DKIM signing to each of those sources.
- Set DMARC to p=none and let aggregate (RUA) and forensic (RUF) reports run for 30 to 60 days before changing anything.
- Move to p=quarantine once reports show clean alignment, then to p=reject.
CISA's phishing guidance frames staged enforcement, monitoring first, then quarantine, then reject, as the safest path to avoid blocking legitimate mail from forwarders or third-party senders. Mailing lists and forwarding services often break SPF alignment, so check each third-party sender's own DMARC documentation before tightening policy, and consider a dedicated subdomain for high-risk bulk senders.
Pro Tip: Use a DMARC report parser rather than reading raw XML. It turns weeks of aggregate reports into a short list of senders you still need to fix.
User training and phishing simulations
Technical controls stop most attacks, but the ones that get through rely on a person clicking, so training has to change behaviour, not just check a compliance box.
Role-based modules work better than one-size-fits-all sessions: finance staff need wire-fraud scenarios, executives need deepfake and CEO-impersonation examples, and general staff need the basics of spotting a spoofed sender. Our employee cybersecurity training guide outlines modules by role, and our guide to common employee cybersecurity vulnerabilities catalogues the failure patterns that show up most often in simulations.
- Run simulations monthly, not quarterly, but vary difficulty and theme to avoid training people to recognize only your test template.
- Put a one-click phish-report button in the mail client and route it straight into your remediation pipeline.
- Track click rate, time-to-report, and repeat-offender rate as your core KPIs.
- Follow up individually with repeat clickers rather than relying only on group training.
Business Email Compromise produced 21,442 complaints to IC3 in 2024, with US$2.77 billion in reported losses, a reminder that the cost of a single successful phish can dwarf a year of training budget.
Detection and post-delivery remediation
Some malicious messages will reach inboxes no matter how good your filters are, which is why what happens after delivery matters as much as what happens before it.
Attachment sandboxing detonates suspicious files in an isolated environment before they reach a user, and link rechecking re-scans URLs at the moment someone clicks rather than only at delivery time, catching links that turn malicious after they pass initial screening. Behavioural analytics and language-based detection add another layer by flagging the writing patterns and urgency cues common in AI-generated impersonation attempts, even when the sender address looks legitimate.
- Enable mass-purge capability so a confirmed malicious message can be pulled from every mailbox at once.
- Set automated remediation thresholds so a handful of employee reports on the same message triggers removal without waiting for manual review.
- Re-check URLs at click time, not just at delivery.
- Log every remediation action for later audit and metrics.
Pro Tip: Connect your phish-report button directly to your remediation tool. Every manual step between a report and a purge is time attackers use to spread.
Incident response for email incidents
A compromised mailbox or a convincing BEC attempt needs a response measured in minutes, not meetings, so write the playbook before you need it.
- Contain immediately: revoke active sessions and tokens, force a password reset, and block the sender domain or malicious URL at the gateway.
- Purge: remove the message from every mailbox it reached, not just the one that reported it.
- Collect evidence: preserve headers, authentication logs, and a timeline of account activity before anything is overwritten.
- Coordinate: loop in finance immediately for wire-related BEC, and legal or PR if customer or employee data may be exposed.
- Remediate and notify: fix the entry point, notify affected parties where required, and retrain the specific team involved.
- Update detection rules based on what the incident revealed, so the same technique is caught automatically next time.
Our 90 Day Plan for Business Email Compromise Prevention walks through this sequence in more operational detail, and our enterprise incident response checklist extends it for larger environments with multiple response teams.
Encryption and transport protection
Transport Layer Security (TLS) protects messages while they move between mail servers, which covers most everyday email but not what happens once a message lands in an inbox or gets forwarded.
S/MIME and OpenPGP add end-to-end encryption and sender signing, so the message body stays unreadable to anyone but the intended recipient, even if a mail server in between is compromised.
- Enforce a minimum TLS version on all mail connectors and monitor certificate expiry so encrypted transport never silently falls back to plaintext.
- Reserve S/MIME or OpenPGP for messages carrying protected health information, legal documents, or financial records where confidentiality matters more than convenience.
- Expect friction: certificate and key distribution across an organization is the main reason end-to-end encryption stays limited to specific use cases rather than every message.
Policy, DLP and mailbox hygiene
Good policy settings catch the quiet failures that filters and training miss, like a forwarding rule an attacker planted months ago.
- Add external sender banners so recipients see at a glance when a message originates outside the organization.
- Disallow auto-forwarding to external addresses, a tactic IC3 guidance flags as a common fraud persistence mechanism, and log every mailbox setting change for at least 90 days.
- Apply outbound data loss prevention rules that detect patterns like PHI or payment card numbers and hold those messages for review.
- Audit forwarding rules, mailbox delegations and orphaned accounts quarterly, since attackers often hide inside a forwarding rule rather than inside a single stolen email.
Nexus playbooks and how we help operationalize these controls
We built our 90 Day Plan for Business Email Compromise Prevention and our employee cybersecurity training guide around the exact checklist above: authentication first, DMARC enforcement second, training and remediation running continuously alongside both.
For teams without the internal bandwidth to run all of this in-house, the highest-value things to hand off first are:
- DMARC report parsing and the staged move to p=reject.
- Attachment sandboxing and automated post-delivery remediation.
- Incident response retainer coverage for the first hours after a suspected compromise.
Cybersecurity and compliance services can be provided with consolidated detection and defined service levels, which matter most in the first hour of an incident, when coordination speed decides the outcome.
A senior executive's take on sustaining email security
Most email security failures are not technical, they are organizational: nobody owns the DMARC rollout past week one, and nobody measures whether training actually changes click rates. Pick an owner for each control, put a date on your DMARC enforcement timeline, and track the numbers monthly. Programmes that stall almost always stalled on ownership, not technology.
— Nick - Sr. Executive
Get help putting this plan into action
These services consolidate pieces of the playbook, threat detection, compliance support, and incident response under one contract to avoid managing multiple vendors to close one gap.
If your team is still working through DMARC enforcement, phishing-resistant MFA, or a formal incident response plan, services are available to cover each piece individually or as one program:
- Cybersecurity assessments and real-time threat detection
- Compliance support for frameworks
- Data protection, backup and disaster recovery planning
- Incident response retainers and a defined rollout plan
Visit our services page to request an assessment or ask about our 90-day Business Email Compromise prevention plan.
FAQ
What is the single most effective email security control?
Phishing-resistant MFA on privileged accounts delivers the fastest risk reduction, since most account takeovers start with a stolen or phished credential. CISA recommends FIDO or PKI-based MFA for administrators first, then wider rollout.
How long should DMARC stay at p=none before enforcement?
Most organizations monitor DMARC reports for 30 to 60 days at p=none before moving to quarantine and then reject. CISA's phishing guidance recommends this staged approach to avoid blocking legitimate mail.
What's the difference between SPF, DKIM and DMARC?
SPF authorizes which servers can send mail for your domain, DKIM signs messages to prove they weren't altered, and DMARC tells receiving servers what to do when either check fails. NIST's technical note covers how the three work together.
How costly is Business Email Compromise?
BEC generated 21,442 complaints to IC3 in 2024, with US$2.77 billion in reported losses for that year. It remains one of the highest-loss categories of cybercrime tracked by federal reporting.
Does Nexus offer email security services?
Yes, our cybersecurity and compliance services include email authentication rollout support, phishing-resistant MFA deployment, and incident response planning. Pricing for these services is available on request through our services page.
Sources
- Public service announcement: IC3 — Business Email Compromise losses (2024)
- Email authentication mechanisms: DMARC, SPF and DKIM — NIST technical note
- Implementing phishing-resistant MFA — CISA fact sheet